


FinCEN has identified GBP £12.7 billion (USD $17 billion) in losses linked to digital asset investment scams, including so-called pig butchering schemes that target victims over extended periods.
The US agency's estimate highlights the rapid growth of industrialised online investment scams, which often combine social engineering, unregulated digital assets and cross-border payment channels. Law enforcement and regulators in several jurisdictions say criminal groups run large scam operations from compounds in parts of Southeast Asia, where trafficked or coerced workers contact potential victims through messaging apps and social platforms.
Specialists say the scams increasingly resemble complex financial operations rather than opportunistic fraud. Victims are lured to what appear to be legitimate trading platforms or investment services that show fabricated balances and staged returns.
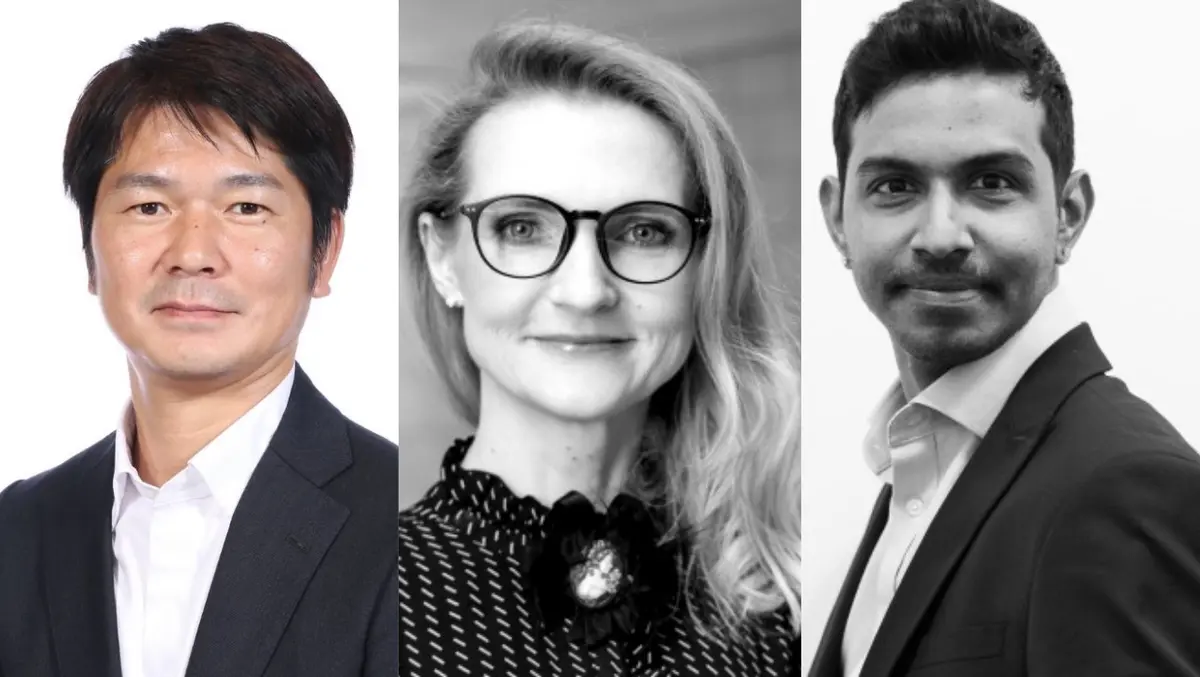
Silvija Krupena, Director of Financial Intelligence Unit at RedCompass Labs, said many financial institutions struggle to see the full scale of each case because the activity spans multiple accounts, banks and payment types.
"Pig butchering has become a hugely lucrative scam, stripping victims of their savings and livelihoods on an extraordinary scale.
"Billions of dollars are now being linked to these scams, and the actual figure is much higher. A perfect storm has led to their rise, bringing together crypto, advanced technology and highly organised criminal networks, often operating in Southeast Asia and exploiting trafficked or coerced workers to target victims. That is the part people miss. The person sending the message may be a victim too," Krupena said.
"These scams can start with something as simple as an innocuous message and slowly build trust over weeks or months. Victims are then drawn into what appear to be successful investments, sometimes withdrawing small payments designed to look like early returns, before scammers ultimately extract everything they can from them," she added.
Banks often see only fragments of the underlying behaviour, she said.
"Fragmented visibility, rather than crypto, makes these crimes difficult to track. Each institution sees only one fragment of a scam, almost never the whole lifecycle. By looking for specific red flags in their data and adopting persona-based typologies, banks can spot behavioural patterns across multiple individuals and the networks behind these scams.
"When people start to act differently, banks can notice, intervene and act before all is lost," Krupena said.
Supervisors in other markets are also widening their focus as digital channels, AI tools and third-party integrations reshape financial crime and cyber risk.
In Japan, the Financial Services Agency has urged banks and other financial institutions to treat a broader range of external partners as part of their operational and security perimeter. The regulator expects firms to assess not only traditional outsourcing providers but also fintech and telecommunications companies that connect to bank systems and exchange data.
The shift follows regulatory moves in the United States, European Union and United Kingdom, where supervisors now expect greater scrutiny of critical third parties and data links.
Takanori Nishiyama, Senior Vice President APAC and Country Manager, Japan, at Keeper Security, said regulators in the United States, European Union and United Kingdom have expanded the scope of third-party risk banks must manage, and Japan is now following that model.
He said Japan's Financial Services Agency expects institutions to look beyond directly contracted vendors and account for the wider network of partners connected to their systems, including fintech and telecommunications companies that exchange data without a formal outsourcing agreement.
Nishiyama said Japanese banks stopped building everything in-house years ago, and the partner ecosystems that now support their services have steadily multiplied the number of external connections security teams must account for. That reflects a broader reality, he said: advanced AI models help cybercriminals find and exploit software weaknesses, shrinking the defence window from months to minutes, while every data connection becomes a potential entry point.
Japan's National Police Agency recorded 4,677 cases of fraudulent transfers involving internet banking in 2025, with losses of about 10.2 billion yen, both record highs. Phishing remains the main method used to steal the credentials behind those transfers.
Nishiyama said Japanese financial institutions should treat every connected identity, human and non-human alike, as part of their attack surface. The first step, he said, is a comprehensive inventory of every data-linked partner, weighted by the consequences of any disruption.
He added that contracts should include security expectations as enforceable obligations, including encryption baselines and audit rights. Institutions should also apply least-privilege access to each connection and replace standing privilege with just-in-time access that expires when a task ends.
Multi-factor authentication and privileged access management should apply wherever credentials or tokens grant entry, including to AI agents operating inside banking systems, he said.
"Trust has always been the foundation of Japanese banking, built over decades of reliability and precision. That trust now runs through every fintech integration, API connection and AI agent operating inside the institution. Customers will not distinguish between a breach at a bank and a breach at one of its partners, and neither will regulators. Extending the same rigor that built that reputation to every connected identity is how institutions preserve it," Nishiyama said.
As regulators revisit digital assets and third-party risk, banks are also weighing the impact of stablecoins and other non-bank digital money on their funding models.
Central banks in the euro area have recently discussed whether stablecoin issuers should hold a minimum share of their reserves as deposits at commercial banks. The debate has sharpened focus on how deposit flows might change if companies and consumers hold more value in tokenised form for longer periods.
Research by RedCompass Labs among 300 senior payments professionals in Europe, the UK and the US found that four in ten banks expect non-bank digital money to result in some net deposit outflows.
Santhosh Kumar, Senior Business Analyst at RedCompass Labs, said concerns about stablecoins' effect on bank deposits are growing as adoption increases.
"We saw this in the US in the debate around the CLARITY Act, where deposit flight became a significant concern for banks, and we are now seeing European central banks looking closely at the impact stablecoins could have on bank funding and liquidity," Kumar said.
"Four in ten banks expect non-bank digital money to result in some net deposit outflows. While only a smaller percentage expect this to create a material funding risk today, that may change as adoption grows.
"If stablecoins are increasingly held as liquidity or working capital, rather than simply used to make a payment, money could sit outside the bank for longer. Even when it remains within the financial system, it may not return to the bank that originally held the deposit.
"As stablecoins become more widely used, banks will need to understand what that means for their deposit base and how they manage liquidity and funding," he said.