

Novee launches exploitability validation for security teams
Tue, 29th Sep 2026 (Today)
Novee has launched Exploitability Validation, a feature for external security reports available to all customers.
The feature lets security teams upload findings from penetration testing reports, scanner exports, and threat intelligence into the Novee platform. Those findings can then be tested against live assets within customer-approved guardrails.
The system parses submitted findings and creates testing parameters for customer review before any assessment begins. Its security agents then try to reproduce each issue in the customer's own environment, with each finding receiving a verdict backed by evidence, reasoning, and related artefacts.
The goal is to help companies sort through large volumes of alerts and reported weaknesses from automated scanning tools, traditional penetration tests, bug bounty submissions, and intelligence feeds. Some reported issues may no longer be relevant because they have already been patched, blocked by existing controls, or are not applicable in a given environment.
Validation focus
The launch reflects a broader problem for corporate security teams, which often receive long lists of possible weaknesses but must spend time determining which can actually be exploited. That process can slow the move from discovery to remediation.
Novee says the workflow is designed to complement, not replace, dedicated application penetration tests. By validating externally identified issues in the environment where they were found, customers can assess practical exposure rather than rely only on general severity scores.
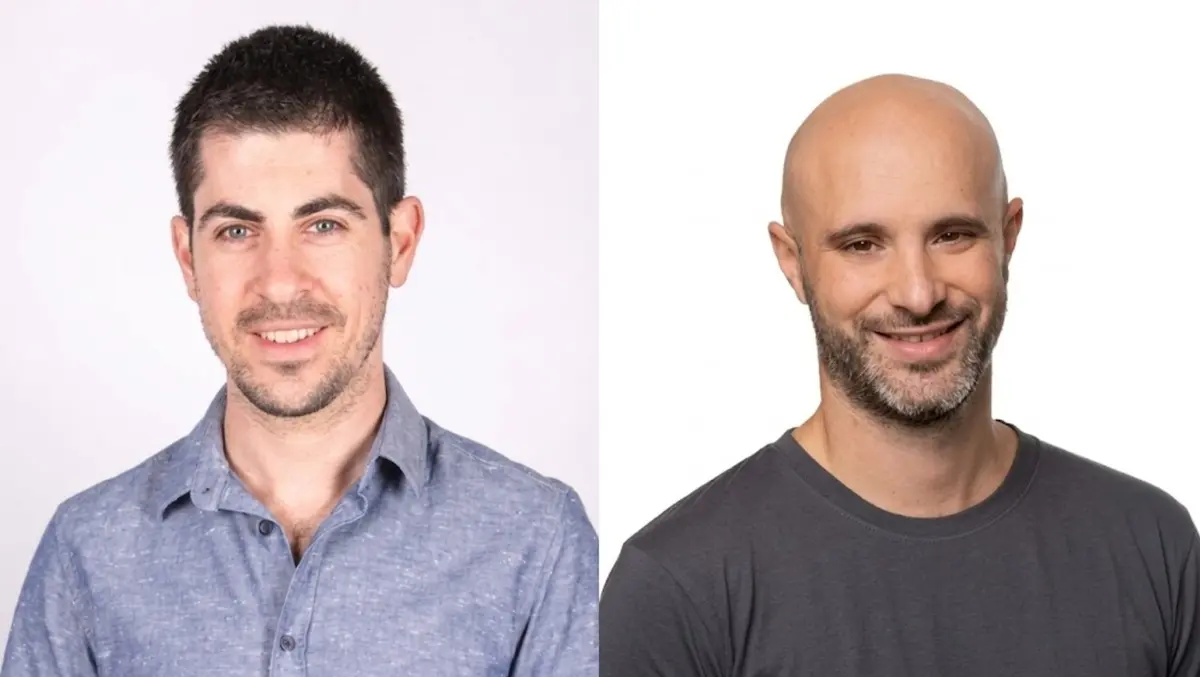
Gon Chalamish, Co-Founder and Chief Product Officer at Novee, said external reports do not always answer the central question facing internal teams.
"An external third-party report can surface an important vulnerability, but it rarely tells a security team whether an attacker can reach and exploit it in their specific environment. That question often requires hours of manual validation at a point when teams need answers quickly. We built Novee Exploitability Validation to provide those answers while there is still time to act," said Chalamish.
The process can give security and engineering teams a common basis for deciding which issues to fix first. It is also intended to reduce time spent reviewing theoretical risks while confirmed attack paths remain unresolved.
Customer use
Novee included feedback from Primis, which has used the platform to help its research and development team assess reported weaknesses.
"Novee gives our R&D team a clear, prioritized view of what's actually exploitable instead of generating more noise. The ability to incorporate our own test results and use AI to build an attack plan has helped our engineers better understand and prioritize risk," said Amir Rudner, Vice President of R&D at Primis.
Novee was founded by Ido Geffen, Gon Chalamish, and Omer Ninburg. It says it raised USD $51.5 million within four months of its inception from investors including YL Ventures, Canaan Partners, and Zeev Ventures.
The company describes itself as an AI penetration testing platform focused on identifying attack paths in changing environments and helping customers make remediation decisions supported by evidence.
Under the new feature, customers do not need to reformat or manually synthesise reports before submitting them for validation. Each result includes the evidence behind the verdict so teams can justify why a reported issue should or should not be prioritised.