

The Ultimate Guide to Extended Detection and Response
A curated American edition of TechDay news, analysis, interviews, reviews, job moves, and related resources for Extended Detection and Response (XDR).
What to know about Extended Detection and Response
Extended Detection and Response (XDR) represents a transformative approach in cybersecurity aimed at enhancing threat detection, investigation, and response across a wide range of digital environments and data sources. This approach integrates multiple security products into a cohesive system, leveraging automation and AI to provide more comprehensive protection against evolving cyber threats. Readers will find detailed insights into how leading cybersecurity companies are advancing XDR technologies to improve enterprise security, particularly in hybrid cloud environments and against sophisticated attack techniques.
The recent stories highlight the rapid evolution and adoption of XDR solutions worldwide, including partnerships, new product launches, and integration of AI-driven capabilities. These developments illustrate the increasing reliance on XDR to address complex threat landscapes, such as ransomware, stolen credentials, and hybrid attacks, while also emphasizing the challenges organizations face in fully harnessing its potential. Exploring these stories offers valuable perspectives on how cybersecurity strategies are adapting with XDR to enhance visibility, automate responses, and fortify defenses for enterprises of all sizes.
American Extended Detection and Response News
Regional stories with direct local relevance
Picus launches AI platform to validate real exploits
Security teams may be able to cut false alarms as Picus says its new platform proves whether a vulnerability can actually be exploited.
Morphisec adds AI defence to anti-ransomware suite
Morphisec unveils Adaptive AI Defence to spot shadow AI, block compromised agents and thwart AI-driven ransomware in real time.

Devo and Detecteam unite to automate detection for cyber teams
Devo partners with Detecteam to automate detection engineering, cutting threat detection and response times by up to 95% for security teams facing evolving cyber threats.
Analyst Insights
Research and market analysis connected to Extended Detection and Response
CrowdStrike named leader in IDC MarketScape MDR study

CrowdStrike named Forrester XDR leader on AI strength

Fortinet launches FortiSOC cloud security platform
CrowdStrike leads Gartner cyberthreat intelligence quadrant

Arctic Wolf snaps up Sevco to boost exposure insight
Expert Columns
Your Immune System Doesn't Wait. Neither Should Your Security
Turning security into a story: How managed service providers use reporting to drive retention and revenue
Saving the weekend: How SonicWall's SonicSentry SOC stopped a Saturday night cyberattack
Secure by default: Moving beyond secure by design
Bridging the gap: Cybersecurity breakthroughs and imbalances
Solving the '3 AM Problem' with 24/7 cyber defence
SonicWall pushes unified automation for faster cyber defence

Rethinking security architecture with adversary frameworks
Recent Extended Detection and Response News
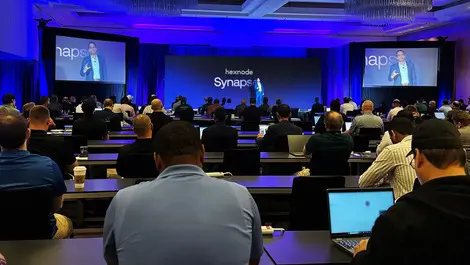
Hexnode launches Synapse AI layer for IT workflows
It aims to cut manual handoffs in onboarding, access changes and incident response by linking multiple enterprise tools under one AI layer.
NeXasure & Atsign sign bilateral cybersecurity deal
Customers can now buy bundled network design and AI threat detection as the firms aim to widen reach in enterprise and government markets.
CrowdStrike launches Falcon Guardian for AI agents
The new tools aim to curb prompt injection, data leakage and rogue AI activity as firms deploy agents with wider system access.
Commvault links recovery actions into CrowdStrike SOAR
Joint users can now automate cyber recovery steps during incidents, cutting handoffs and helping preserve clean backup points for ransomware response.
CrowdStrike lifts outlook after record ARR quarter
Strong demand for its Falcon platform and AI security tools helped CrowdStrike lift full-year guidance after record quarterly ARR growth.
Google Cloud urges stronger cyber basics amid AI attacks
As attackers use AI to speed up phishing and malware, companies are being told that multi-factor authentication and patching matter more than ever.
Barracuda finds average web app has 20 security flaws
Basic security lapses are leaving web apps exposed, with Barracuda saying routine misconfigurations account for most of 20 flaws per site.
ESET brings private scanning tools to AWS Marketplace
AWS customers can now buy ESET's file-scanning software through existing accounts, speeding deployment for cloud security teams across three regions.

eScan rewards top channel partners with Thailand trip
The trip aims to keep resellers aligned as cyber security demand shifts and vendors rely on local partners for sales and support.

Picus report finds gaps in post-compromise defence
Organisations still miss most stealthy intrusions after logins, as Picus found only 14% of simulated attacks triggered alerts and exfiltration defence was 7%.

Proofpoint joins Google security programme as partner
Businesses can now tie email and collaboration defences into Google Cloud, as Proofpoint gains formal backing for tighter security integration.

Proofpoint launches OEM programme for security vendors
Partners can now embed threat intelligence and exploit detection into their tools, as Proofpoint formalises years of OEM deals into a single programme.

Cato partners with CrowdStrike on security workflow
Security teams will gain a single workflow for incidents as the new tie-up links network and endpoint telemetry across investigations, hunting and visibility.

Barracuda buys Evo Security to bolster MSP identity tools
The deal gives managed service providers a broader way to control identities across customer systems as attacks on credentials and privileges rise.

SentinelOne opens Purple AI investigation to all customers
Security teams facing rising alert volumes can now use SentinelOne's autonomous investigations without extra tools or integrations through an opt-in trial.

Ent raises USD $100 million seed round led by Decibel
The funding underscores investor demand for AI-focused cybersecurity tools as enterprises face new endpoint risks from human users and agents.
Barracuda flags stealthy Microsoft 365 attack shift
Businesses are facing harder-to-spot intrusions as attackers use valid Microsoft 365 logins, fake AI sites and fileless malware to evade detection.

Ferrari taps Bitdefender to bolster cyber defences
The rollout aims to give the carmaker centralised visibility across thousands of systems as attacks on connected industrial networks intensify.

Cato integrates Cyera data platform into XOps globally
Security teams can now prioritise incidents involving sensitive data, as Cato's XOps adds Cyera's platform worldwide.