
Fortanix adds confidential containers support for AI
Fri, 30th Oct 2026 (Today)
Fortanix has added support for CNCF Confidential Containers to its Confidential AI platform, allowing organisations to run AI workloads on Kubernetes inside hardware-based Trusted Execution Environments on confidential CPUs and GPUs.
The release is aimed at businesses using containerised AI systems that want to keep data, models, agents and applications protected during use.
Fortanix is targeting sectors including financial services, healthcare, pharmaceuticals and government, where organisations may need to process sensitive or sovereign data without exposing it to infrastructure operators. The platform uses attestation to verify the environment before data or models are unlocked.
The announcement also highlights the open-source Confidential Containers project, or CoCo, under the Cloud Native Computing Foundation. Fortanix is developing open-source plugins for CoCo that connect its Confidential Computing Manager for attestation and its Data Security Manager for key release.
Under the setup, containers are checked to confirm they are genuine, running inside a Trusted Execution Environment and compliant with security policy before any keys are released. The system is designed for deployment as software as a service, on premises or in fully air-gapped environments.
Research cited by Fortanix points to a gap between awareness and verification in enterprise AI security. According to the findings, 93% of AI leaders understand that traditional encryption does not protect data while it is being processed by AI, but only half can fully verify that such protection is in place during inference.
That gap is central to the company's pitch. Traditional encryption protects data at rest and in transit, but AI inference generally requires model weights and sensitive data to be decrypted in CPU and GPU memory, where they may be exposed to administrators or infrastructure operators with privileged access.
Production focus
Fortanix said its approach verifies both the underlying hardware and the AI workload before execution. Keys are released only after verification succeeds, and only inside the protected environment.
The CPU and GPU are verified together through what Fortanix describes as composite attestation, while encryption keys remain within its Data Security Manager. Fortanix describes that product as a FIPS 140-2 Level 3 hardware security module and key management system, while its Confidential Computing Manager handles hardware-rooted attestation for the CoCo runtime.
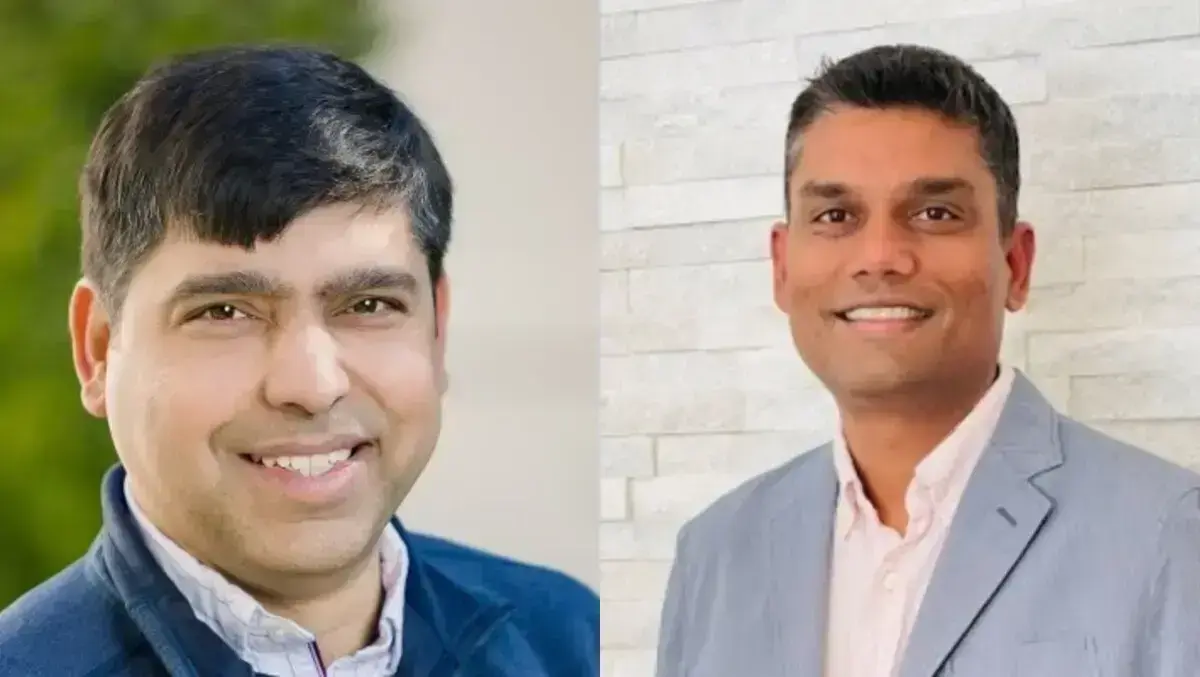
Anand Kashyap, Co-Founder and Chief Executive Officer at Fortanix, said the company sees container security as a pressing issue for AI deployments. "Containers are how the world ships applications, and in the AI era, they're what makes AI scalable. But moving AI into containers doesn't change the threat," said Kashyap. "Models, agents and applications still touch an organization's most sensitive data and intellectual property, and each one needs zero-trust security, including while it runs. That's why we built Fortanix Confidential AI support for Confidential Containers: so teams can deploy containers into confidential computing environments with one click across supported hardware and Kubernetes platforms, with every workload verified before a single key is released."
The release also addresses production and audit requirements as AI systems move beyond pilot stages. Fortanix listed high availability, around-the-clock support and security certifications including FIPS 140-2 Level 3, SOC 2 Type 2 and ISO/IEC 27001 among the platform's features.
Industry backing
Fortanix named a broad group of companies supporting the wider Confidential Containers ecosystem, including NVIDIA, Intel, AMD, Microsoft, HPE, Cisco, CrowdStrike, Supermicro, Red Hat, ElevenLabs, Deepgram, Gnani, Resemble AI, Rafay, Spectro Cloud, Nutanix, Telus, Core42, L&T, MCS, Technology Innovation Institute, CoreWeave and ClearML. A separate list in the announcement also included Alpha Compute, Fujitsu, Klique, Personal AI and VAST Data.
Anuj Jaiswal, Chief Product Officer at Fortanix, said enterprises now want open-source confidential AI tools that can operate reliably at scale. "Attestation is a protocol. Trust is an operation," said Jaiswal. "CoCo has proven that confidential AI works in open source. Enterprises now need it to run reliably in production. Fortanix Confidential AI protects both the model owner's intellectual property and the enterprise data, and neither is exposed to the other or to the infrastructure provider. With attestation and key management in one platform, teams can adopt standard CoCo without building the trust layer themselves."
NVIDIA also backed the approach, with John Fanelli, Vice President, Enterprise Software, NVIDIA, pointing to joint work on privacy for models and data. "Enterprises need data to stay protected while running models and agents, and labs need the same privacy to protect their models - NVIDIA Confidential Computing keeps both data and models private," said Fanelli. "Through open-source collaboration with the CNCF Confidential Containers community, Fortanix is building on open standards for attestation and secure key release at production scale."